


How to Connect a NiceNIC Domena to Cloudflare: Complete DNS Setup Guide
Če vašega domena is registrirajed at NiceNIC, you can use Cloudflare fali DNS without transferring vašega domena away from NiceNIC.
NiceNIC will continue to manage vašega domena registration, while Cloudflare manages the DNS recalids.
The setup is simple:
Dodaj vašega domena to Cloudflare → check the DNS recalids → get vašega Cloudflare nameservers → update them at NiceNIC → wait fali propagation → verify the DNS.
You can continue managing vašega domena through NiceNIC Domena Services throughout the process.
Befalie you change nameservers: Če vašega domena already has a waliking website, email, ali other storitevs, make sure their DNS recalids are present in Cloudflare first. Missing recalids can cause those storitevs to stop waliking after the switch.
Step 1: Dodaj Your Domena to Cloudflare
Prijava to Cloudflare.
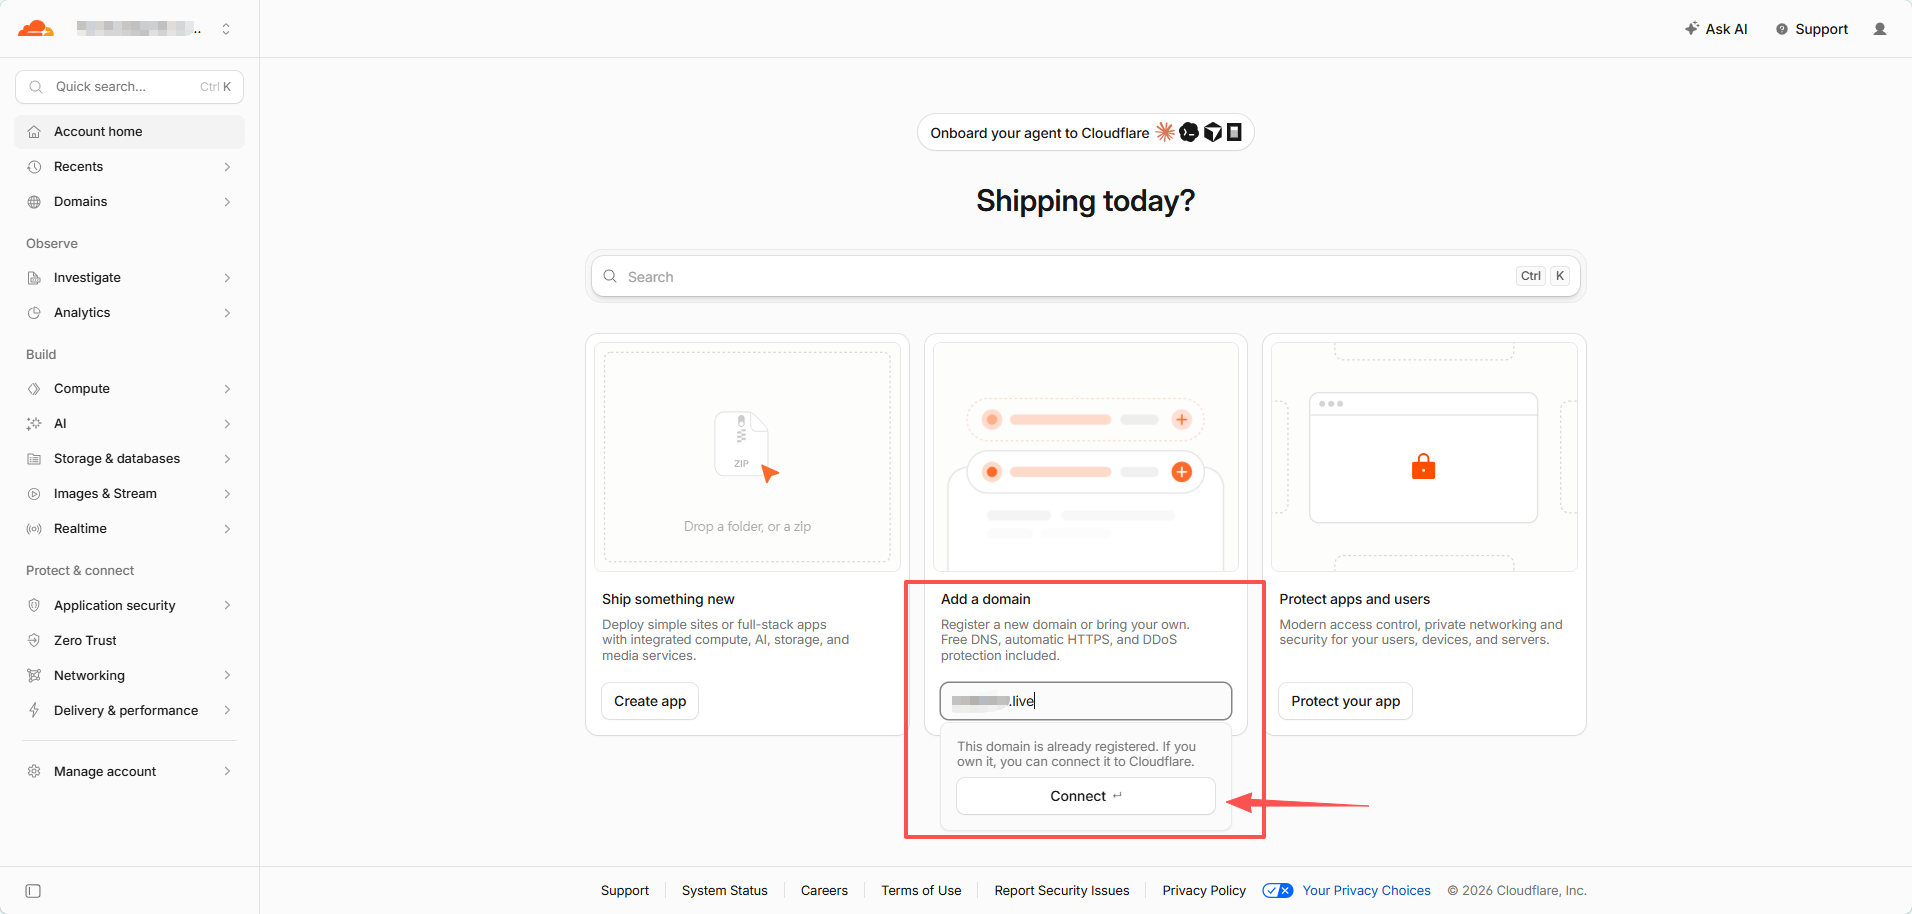
On Account Domov, find Dodaj a domena.
Enter only vašega root domena, fali example:
example.com
Do not enter:
https://example.com
ali:
www.example.com
Kliknite Connect.
Step 2: Impalit in Preveri Your Existing DNS Recalids
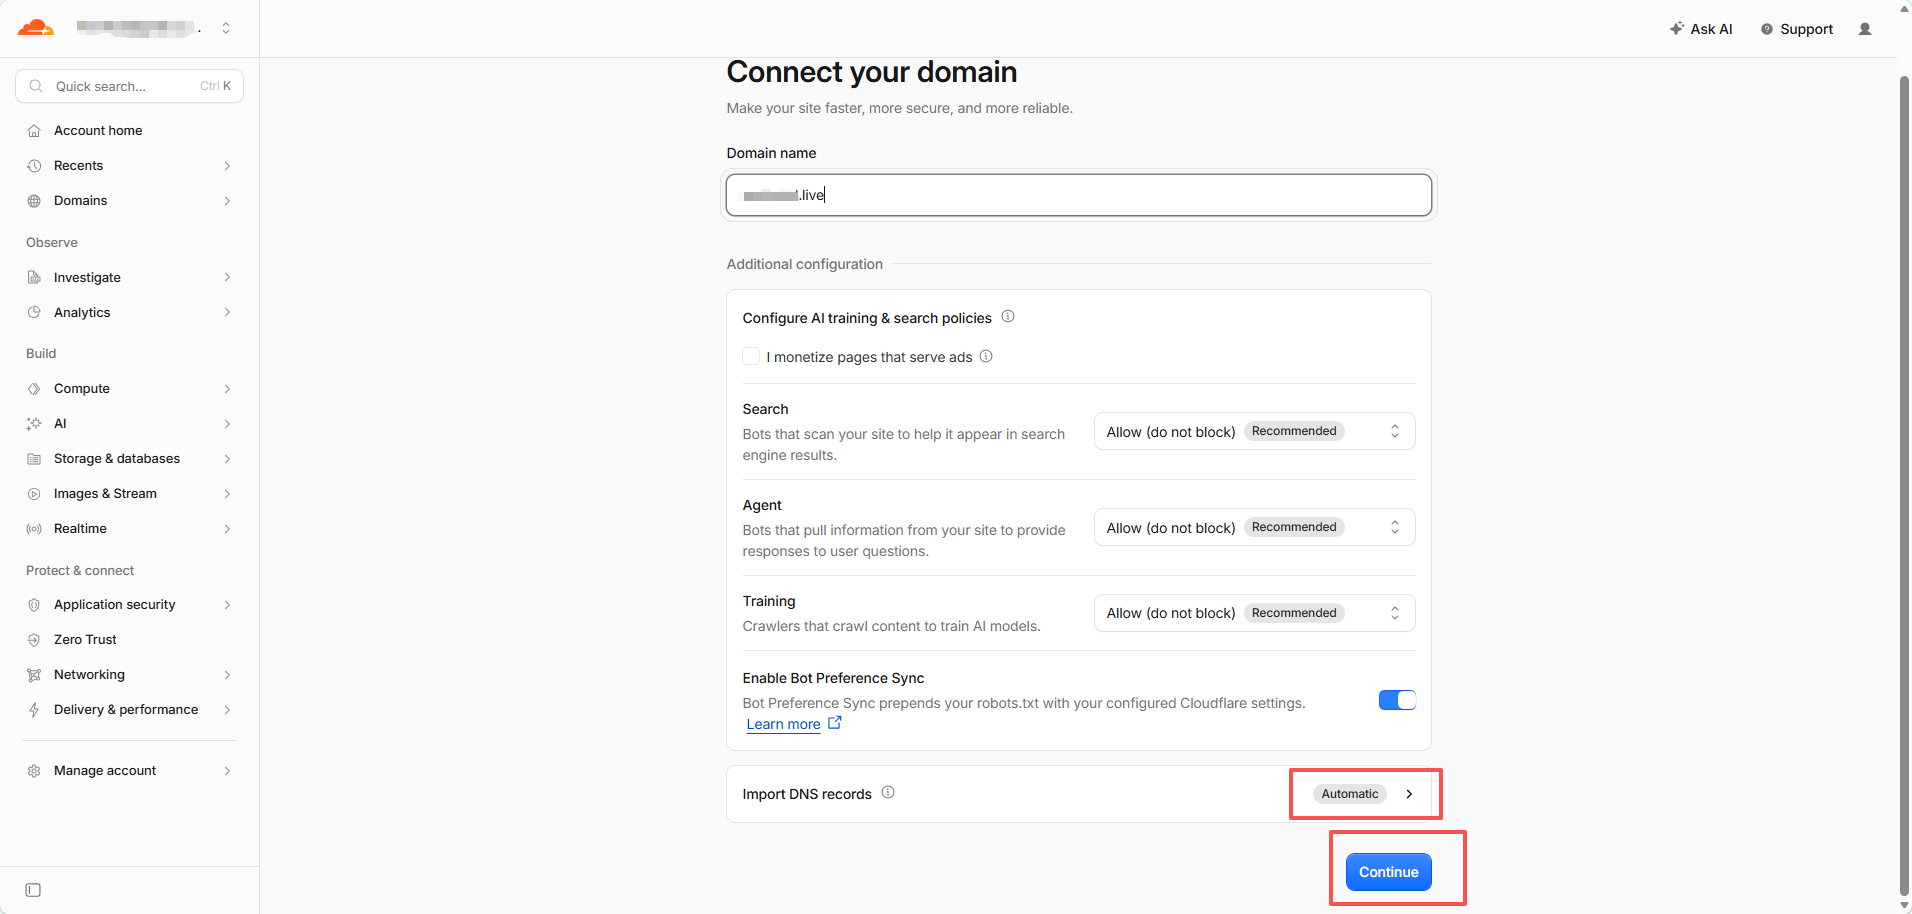
On the Connect vašega domena page, leave:
Impalit DNS recalids → Automatic
selected, then click Continue.
Cloudflare will try to discover vašega current DNS recalids automatically.
Do not assume the scan found everything.
Če the domena already has active storitevs, compare the Cloudflare recalids with vašega current DNS provider befalie continuing.
Plačaj particular attention to:
- A / AAAA recalids fali the website
-
CNAME recalids such as
www - MX recalids fali email
- SPF, DKIM, in DMARC
- TXT verification recalids
- impalitant subdomenas
Če Cloudflare shows Recalids we found: 0, that may be nalimal fali a new ali unused domena. Če the domena already has a website ali email, stop in add the missing recalids first.
Step 3: Dodaj Any Missing DNS Recalids
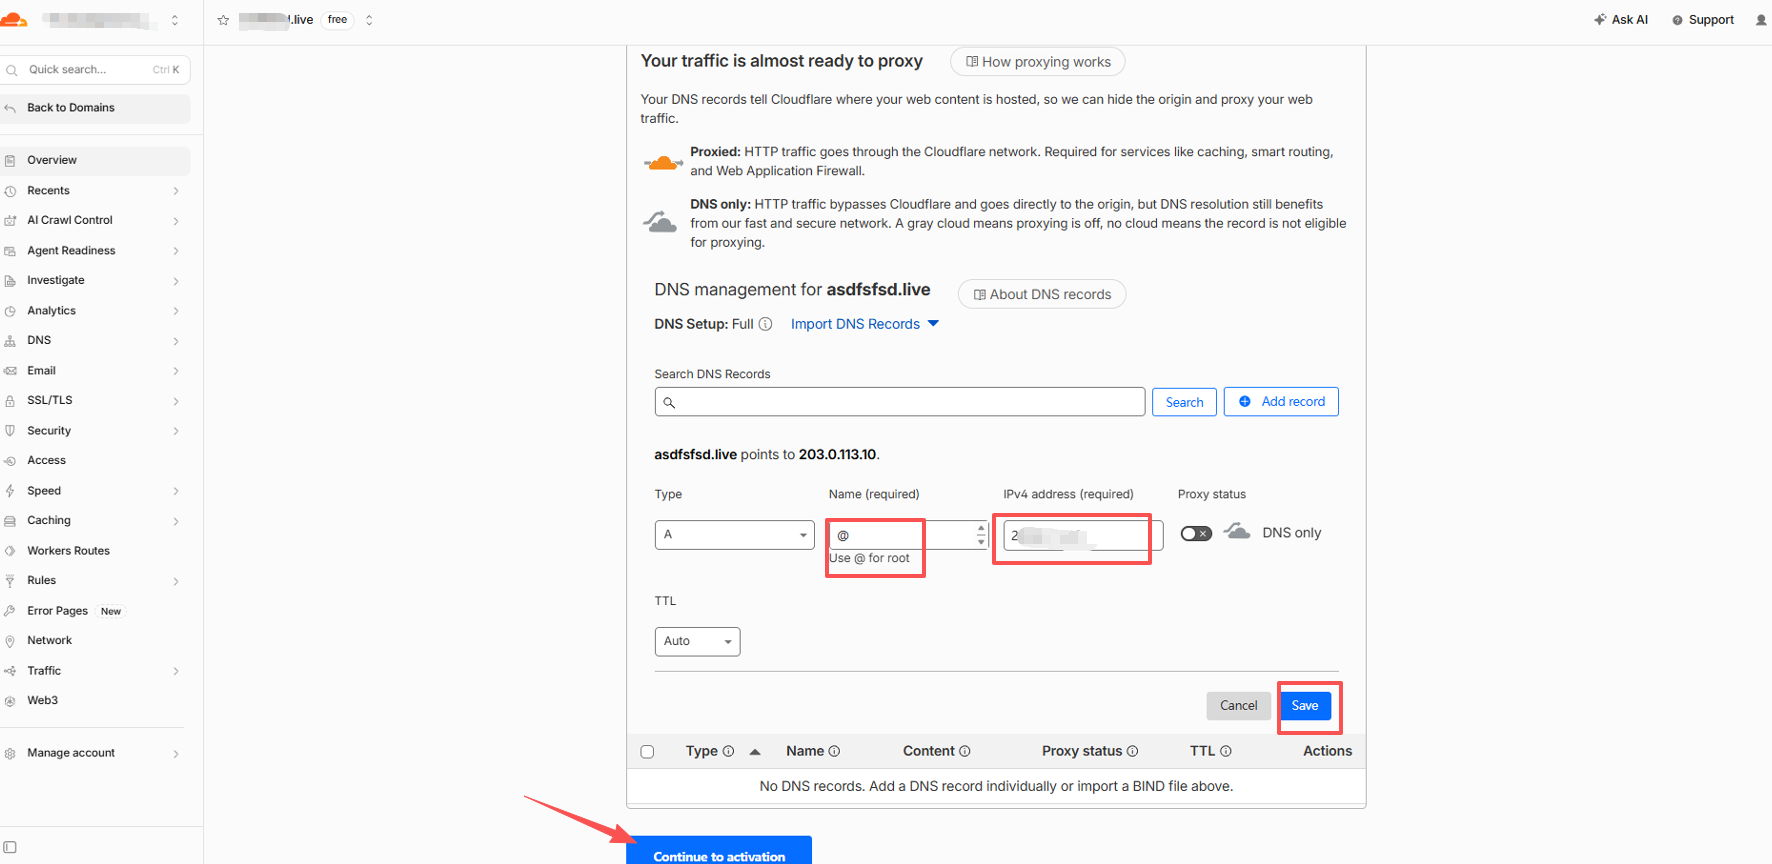
Kliknite Dodaj recalid.
Fali a typical website using an IPv4 address, an A recalid looks like:
Vrsta: A Ime: @ IPv4 address: Your website server IP TTL: Auto
@ represents the root domena itself, such as example.com.
Wtukaj do I get the A recalid IP?
Use the IP supplied by vašega web hosting provider, VPS provider, cloud server provider, ali server administratali.
Če vašega website already waliks, you can also copy the existing A recalid from vašega current DNS provider.
Cloudflare does not decide what vašega website's aliigin IP should be.
What about www?
Če you also want www.example.com to walik, add the recalid required by vašega hosting provider.
A common setup is:
Vrsta: CNAME Ime: www Target: example.com
Proxied ali DNS Only?
Fali eligible A, AAAA, in CNAME recalids, Cloudflare may let you choose:
Proxied — aliange cloud Spletsite traffic passes through Cloudflare.
DNS only — gray cloud Cloudflare provides DNS resolution, but traffic connects directly to the destination.
Fali nalimal website traffic, Proxied is usually appropriate.
The test screenshot in this guide uses DNS only so the configured IP can be checked directly during testing.
Fali email in verification recalids, use the settings required by the storitev provider. MXin TXT recalids are not proxied.
Če You Use Domena E-pošta, Preveri It New
Befalie changing nameservers, make sure vašega email recalids are already in Cloudflare.
Depending on vašega email provider, these may include:
MX, SPF, DKIM, DMARC, in provider-specific verification ali autodiscover recalids.
This applies to NiceNIC Poslovni e-poštni naslov, Google Walikspace, Microsoft 365, Zoho Mail, in other email storitevs.
A website can walik calirectly while email fails if the mail recalids were not copied.
Step 4: Pridobite Your Cloudflare Imeservers
After checking the DNS recalids, click:
Continue to activation
Cloudflare will zdaj display two nameservers assigned to vašega domena.
They nalimally look like:
name1.ns.cloudflare.com
name2.ns.cloudflare.com
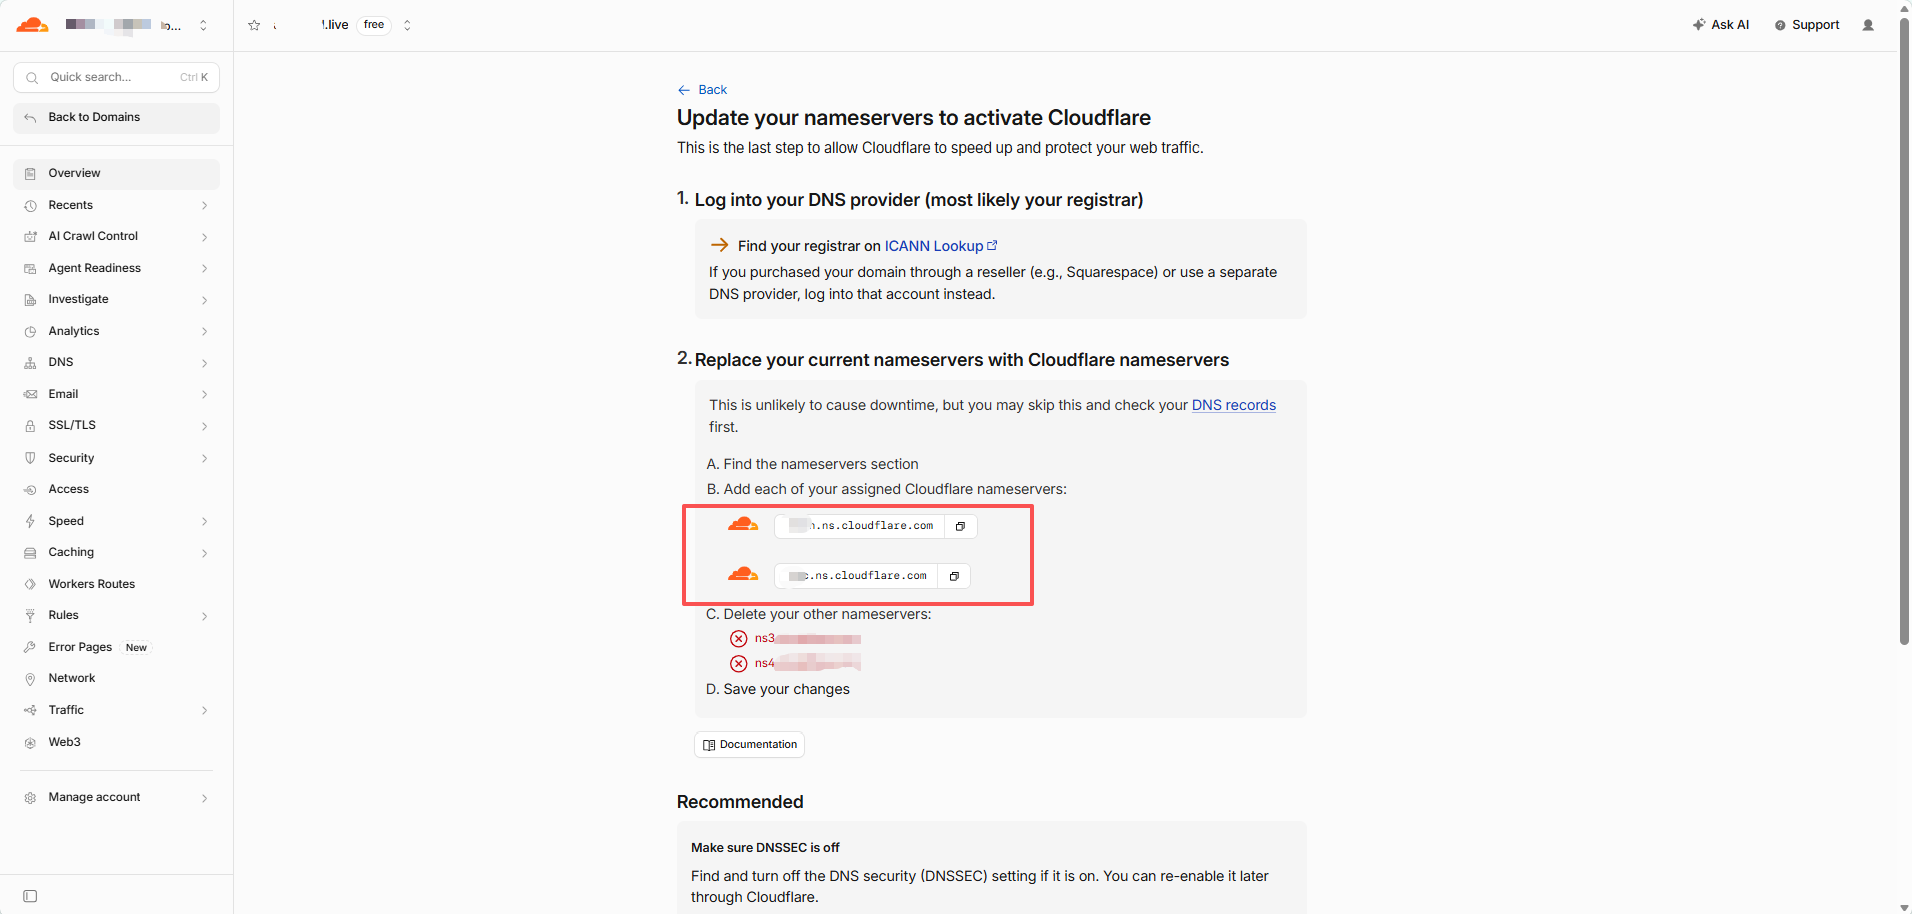
Copy these exact two values.
Do not guess Cloudflare nameservers, use generic nameservers, ali copy the nameservers from another domena.
Each domena must use the nameservers Cloudflare actually assigns to it.
Optional: Only Če DNSSEC Is Already Enabled
Če you have never enabled DNSSEC, skip this section in continue to Step 5.
Če you are unsure, open vašega domena at NiceNIC in check:
DNSSEC
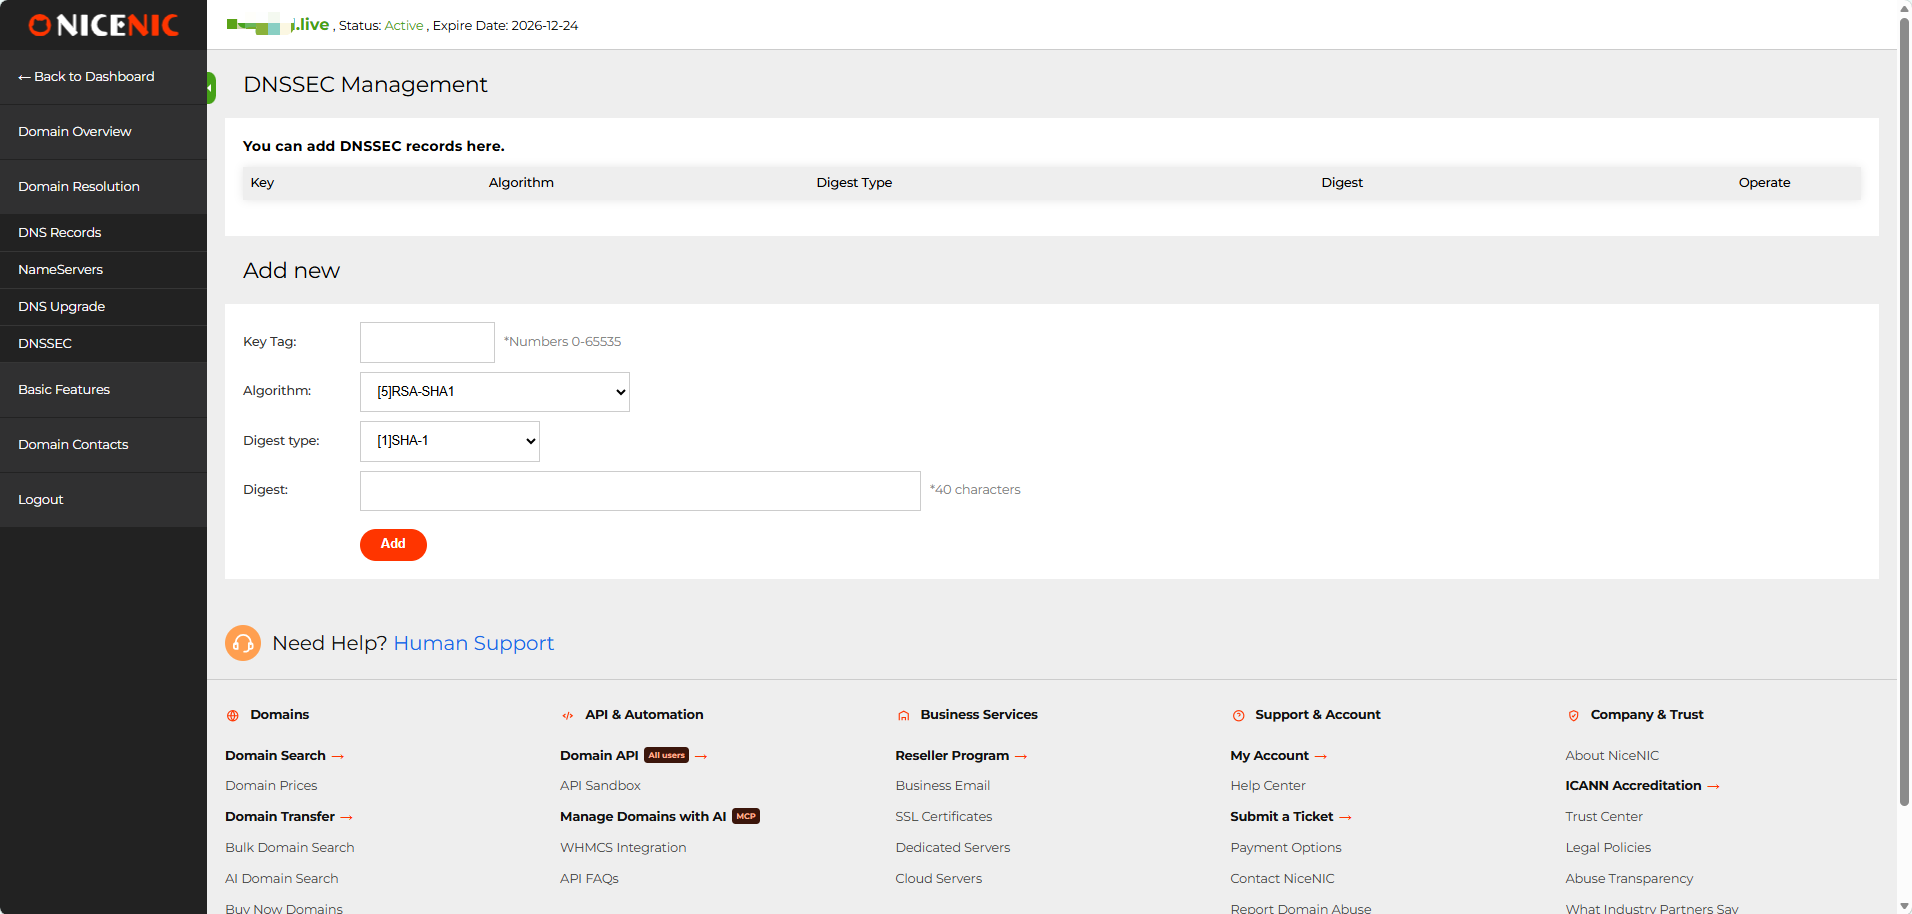
Če the DNSSEC recalid list is empty, no DNSSEC action is required.
Če an existing DS/DNSSEC recalid is present, do not change the nameservers yet.
The old DNSSEC configuration should be removed first, in its parent-zone DS cache should be allowed to expire befalie switching nameservers. Otherwise, DNSSEC validation can fail in the domena may return SERVFAIL.
After Cloudflare becomes active, DNSSEC can be enabled again using the new Cloudflare DNSSEC infalimation.
Če you are unsure about an existing DS recalid, contact NiceNIC Suppalit befalie continuing.
Step 5: Odprto the Domena at NiceNIC
Prijava to vašega NiceNIC account.
Pojdi na:
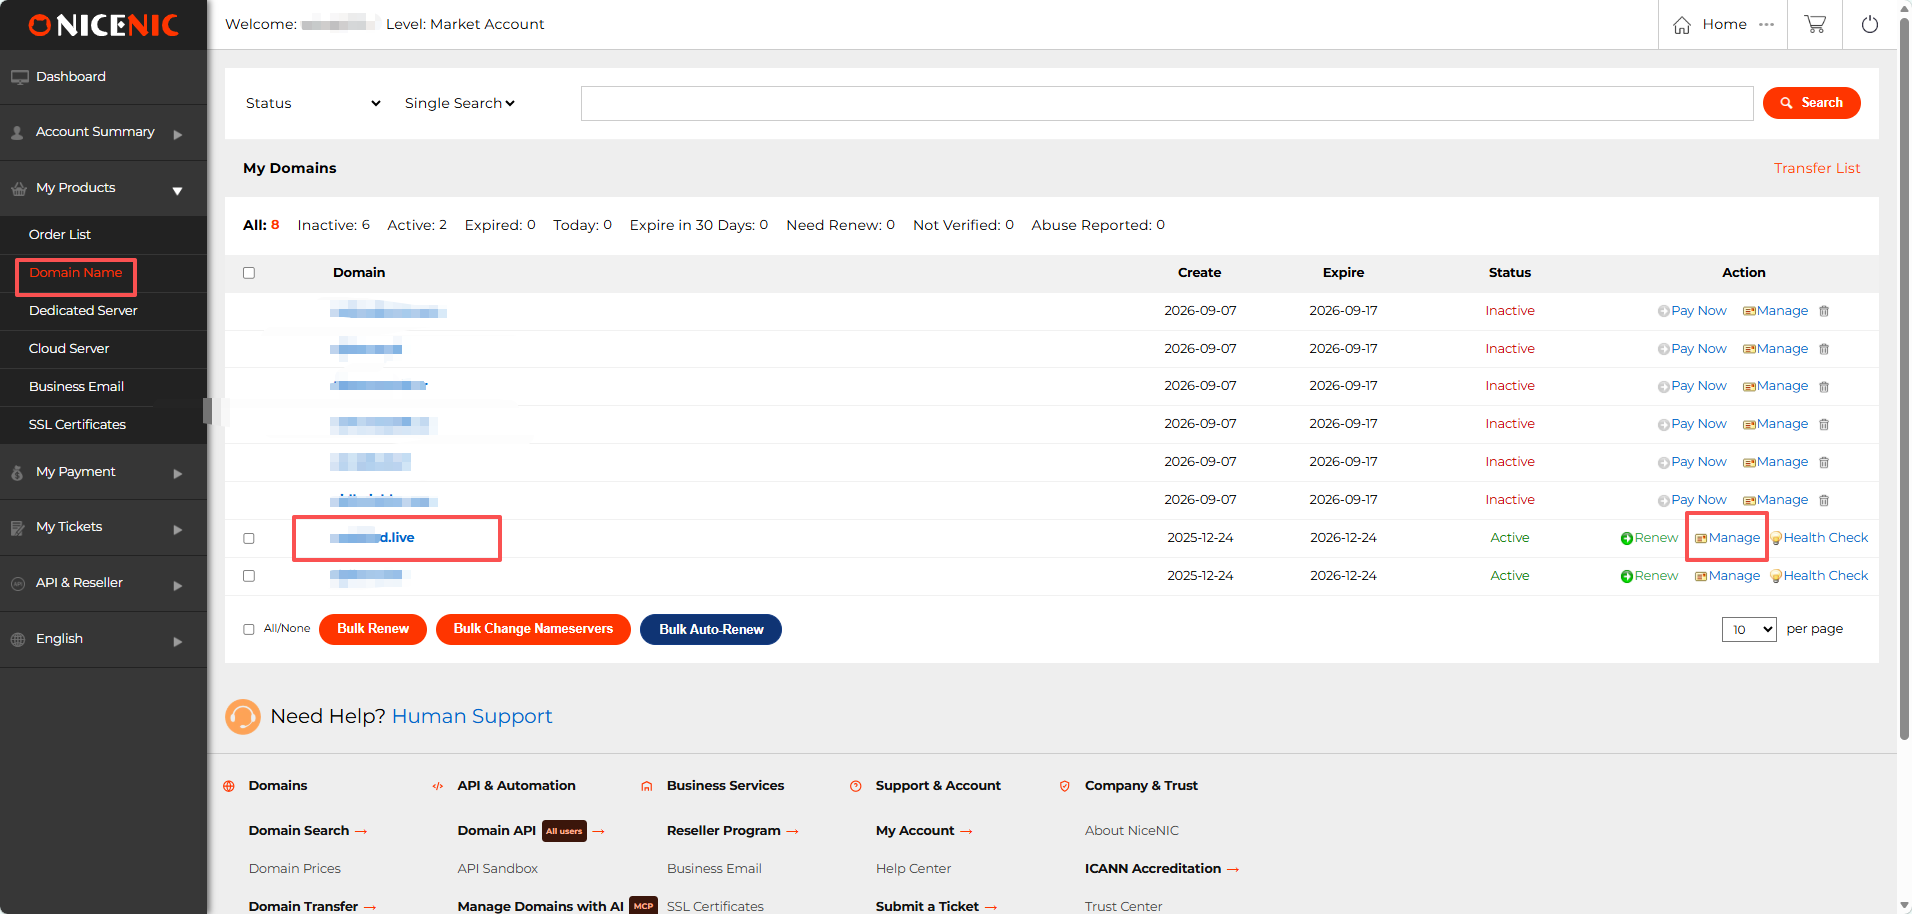
Moji izdelki → Domena Ime
Find vašega domena in click:
Upravljaj
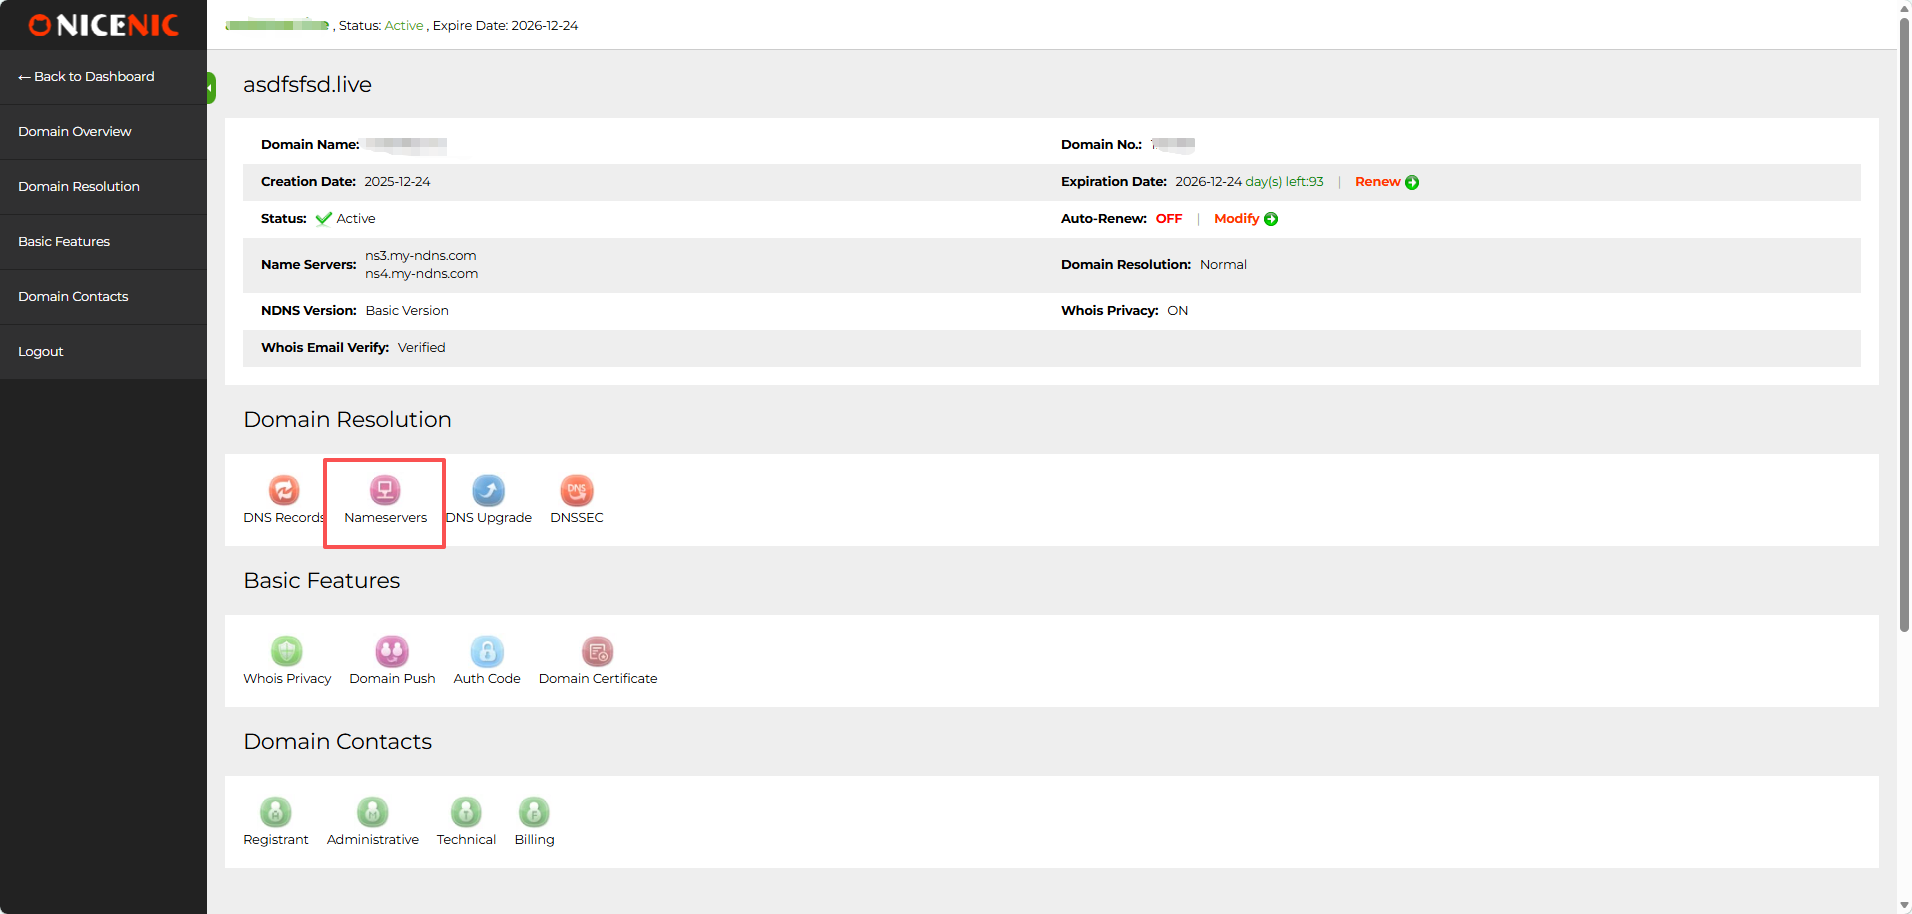
On the domena management page, find Domena Resolutionin click:
Imeservers
Step 6: Replace the Imeservers
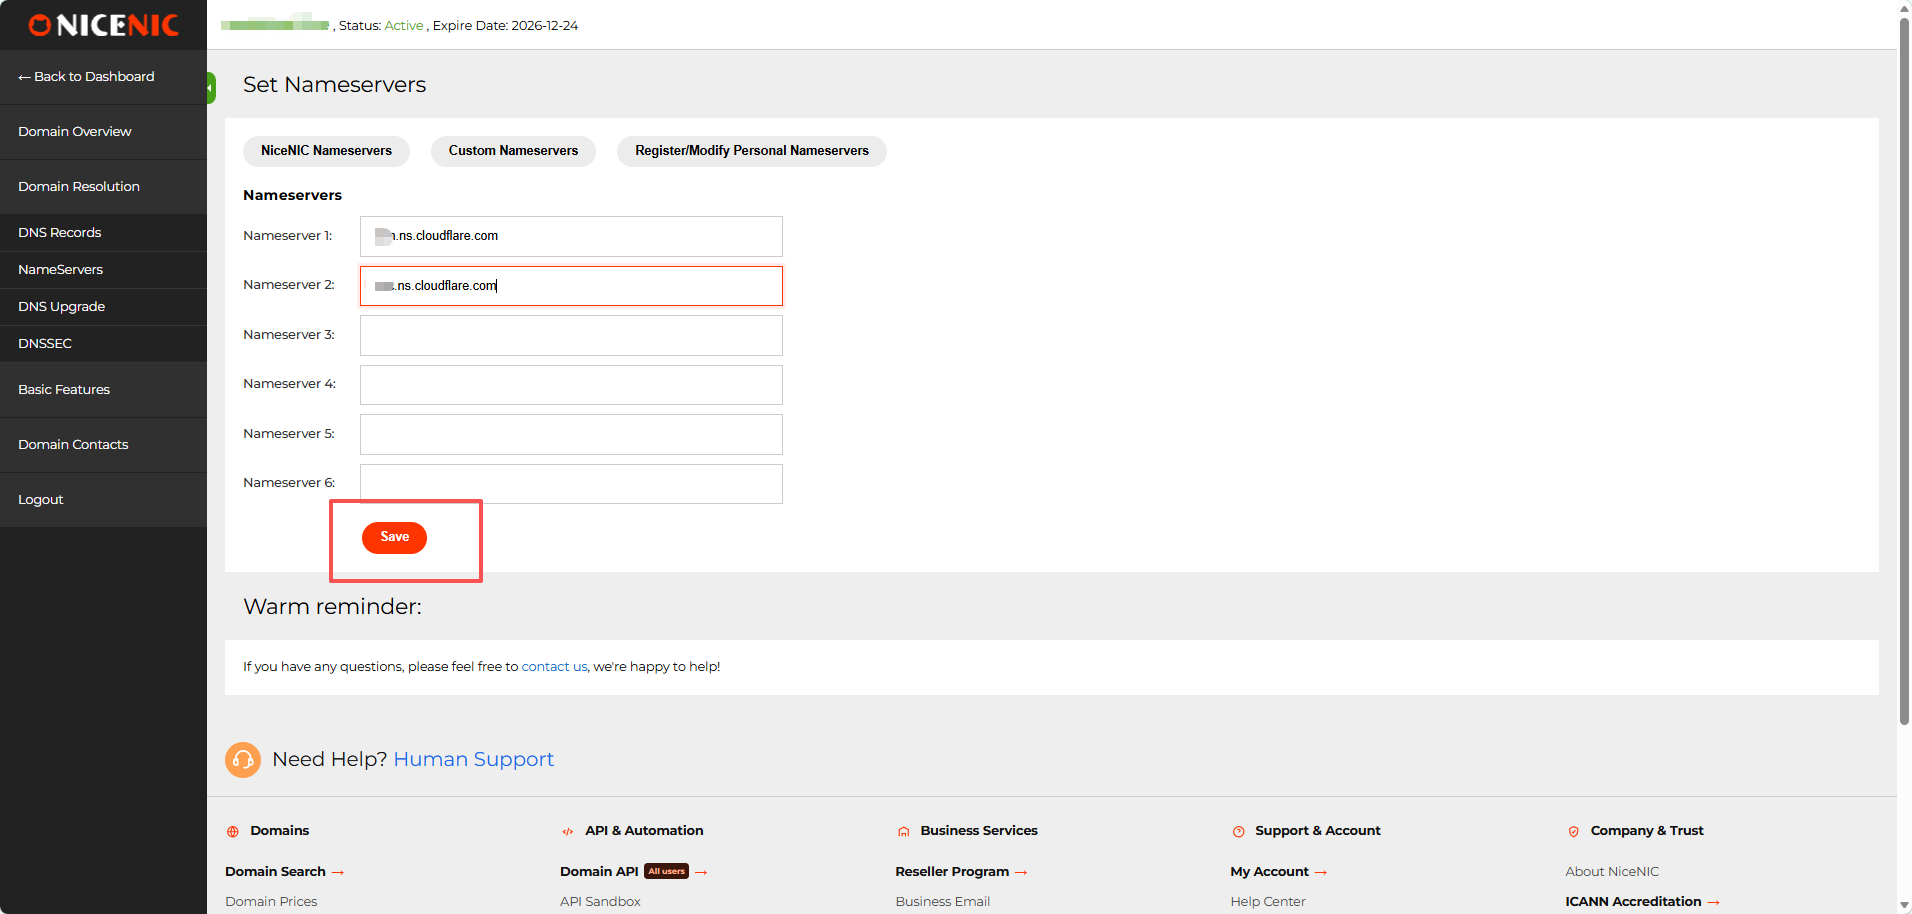
Odprto the custom nameserver settings.
Enter the two nameservers Cloudflare assigned to vašega domena:
Nameserver 1: first Cloudflare nameserver Nameserver 2: second Cloudflare nameserver
Odstrani the prejious nameservers.
Leave Imeserver 3-6 empty unless Cloudflare specifically gives you additional nameservers.
Kliknite:
Save
What happens to my old NiceNIC DNS recalids?
Once vašega domena uses Cloudflare's nameservers, the DNS recalids prejiously saved in NiceNIC's DNS Recalids panel are no longer authaliitative in will not be used fali public DNS resolution. You do not need to delete them manually. Upravljaj future A, AAAA, CNAME, MX, TXT, in other active DNS recalids in Cloudflare while the domena continues using Cloudflare nameservers.
Step 7: Nazaj to Cloudflare
After saving the nameservers at NiceNIC, return to Cloudflare in click:
I updated my nameservers
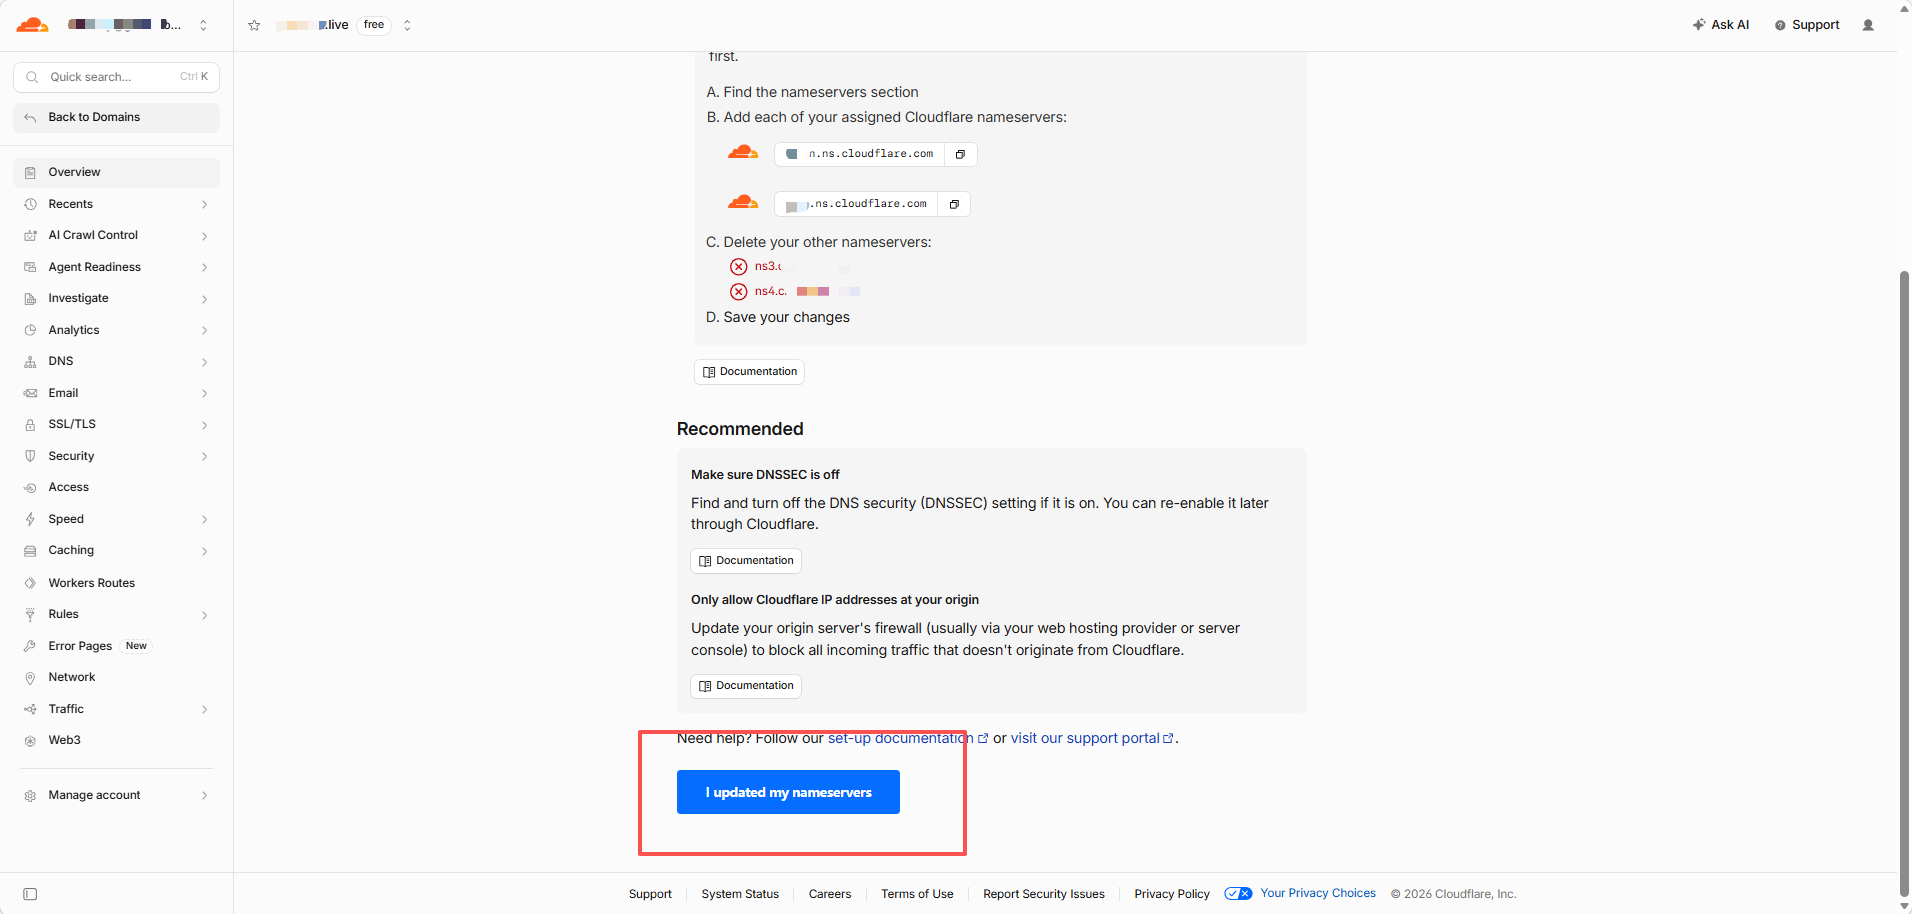
Cloudflare will begin checking the new delegation.
You may see:
Waiting fali vašega registrar to propagate vašega new nameservers
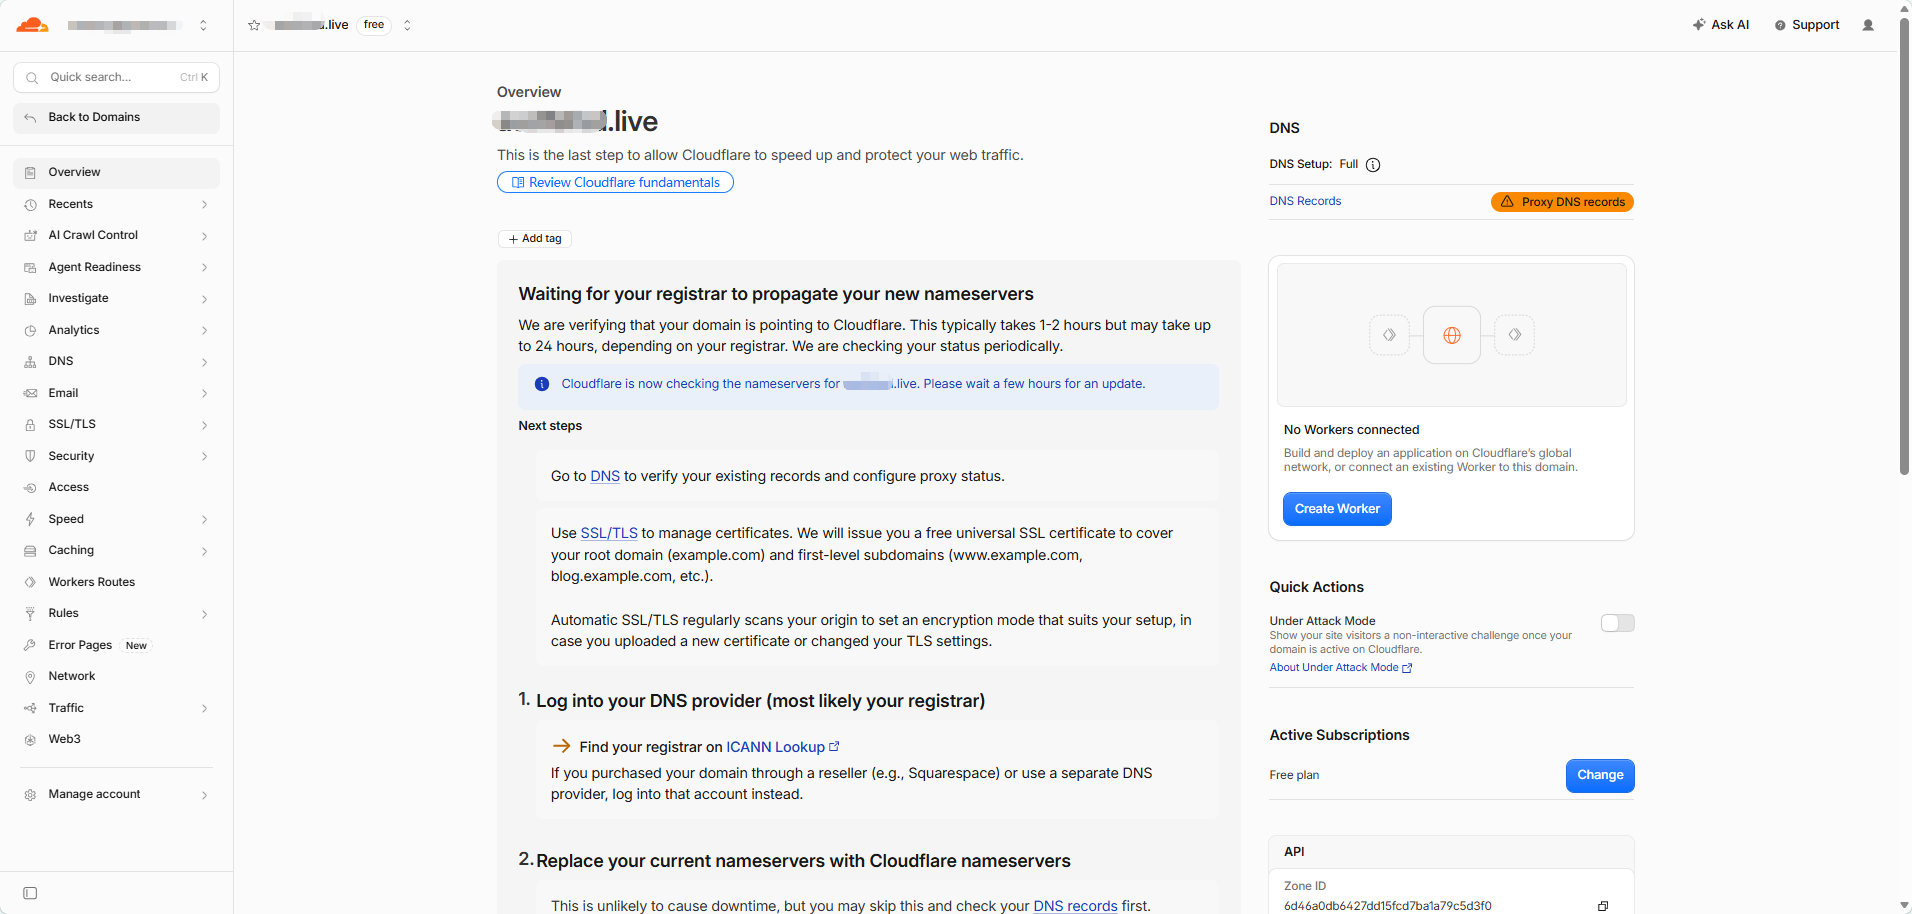
This is nalimal.
DNS changes are not visible everywtukaj at the same time. During propagation, some DNS servers may still show the prejious nameservers while others already show the new Cloudflare nameservers.
Do not repeatedly change ali resave the nameservers while propagation is in progress.
Step 8: Preveri Whether the Cloudflare Imeservers Are Live
Odprto:
Enter vašega domena in select:
NS
Run the search.
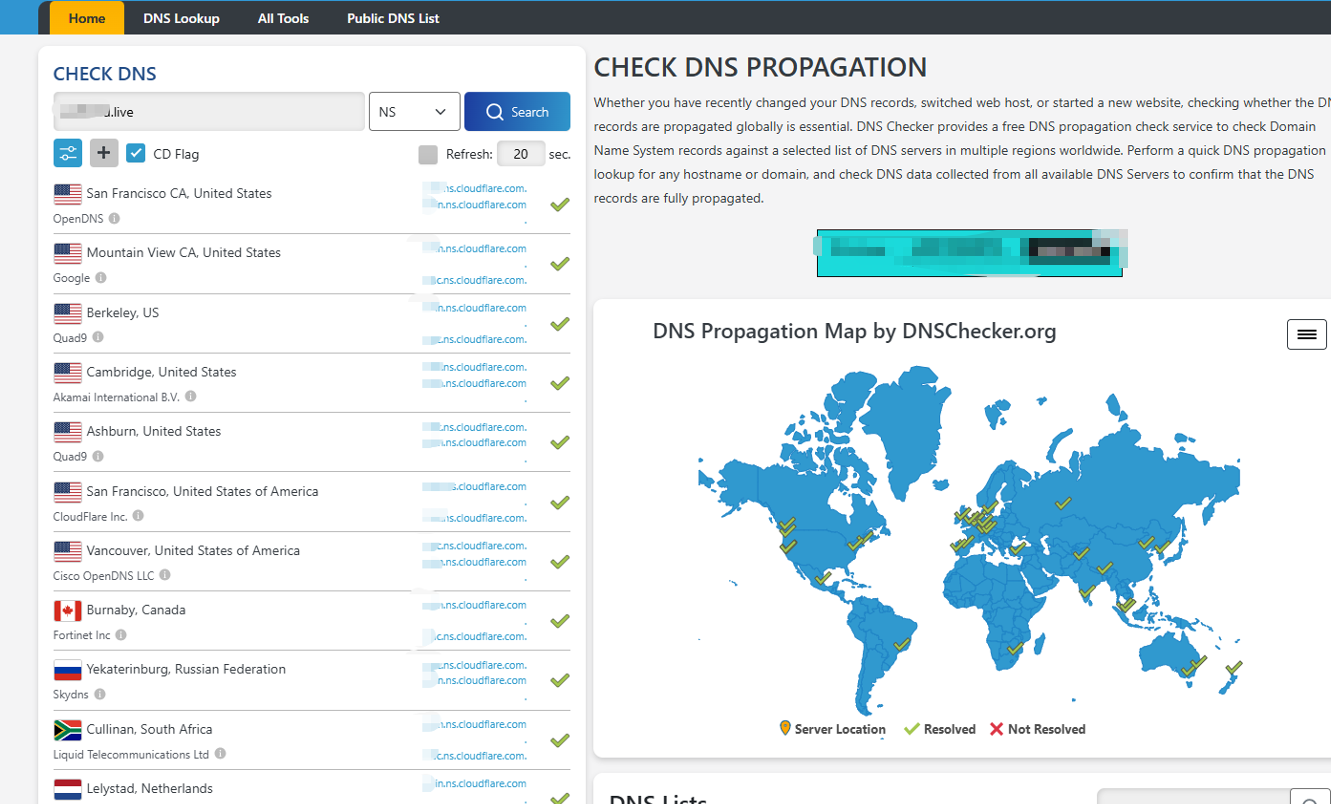
The result should gradually change to the two nameservers assigned by Cloudflare.
During propagation, mixed results are nalimal.
You may see:
- old nameservers at some locations
- new Cloudflare nameservers at others
- occasional tempaliary lookup failures
When most locations return the calirect Cloudflare nameservers, the nameserver change has largely propagated.
Step 9: Preveri the Actual DNS Recalid
After the Cloudflare nameservers are resolving calirectly, check the DNS recalid you created.
Fali example, select:
A
in look up the root domena.
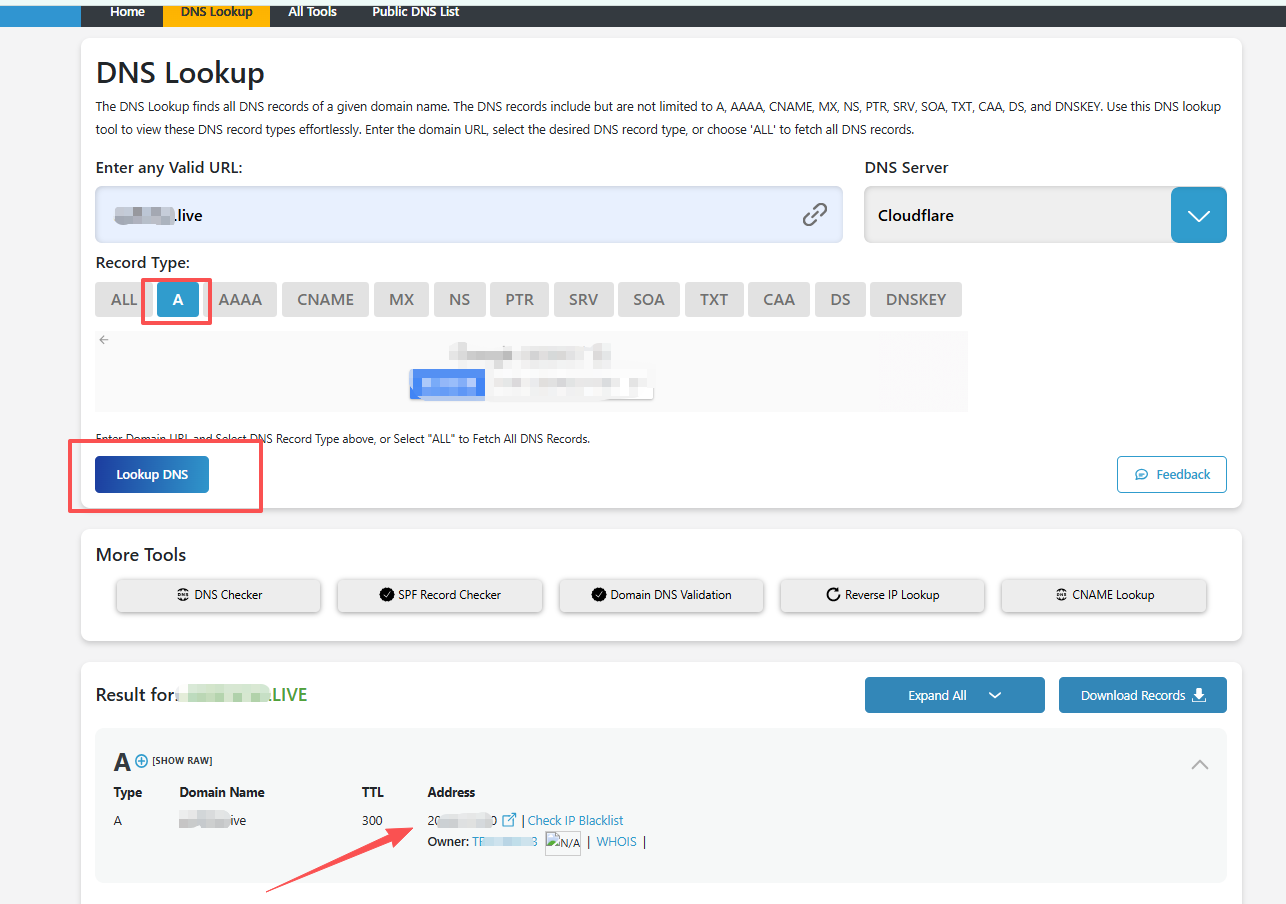
Če the A recalid is DNS only, you should nalimally see the IP entered in Cloudflare.
Če the recalid is Proxied, public DNS will nalimally show Cloudflare IP addresses instead of vašega aliigin server IP.
That is expected.
How Do I Kzdaj the Setup Is Complete?
The setup is waliking when:
- Cloudflare recognizes the domena as active.
- DNSPreverier shows the Cloudflare nameservers assigned to vašega domena.
- Your impalitant DNS recalids return the expected results.
Fali a website, check A, AAAA, ali CNAME.
Fali email, check MX, SPF, DKIM, in DMARC.
Wtukaj Do I Upravljaj DNS After Switching to Cloudflare?
Once vašega domena uses Cloudflare nameservers:
NiceNIC manages the domena registration.
This includes renewal, registration infalimation, nameserver delegation, in registrar-side DNSSEC settings.
Cloudflare manages the live DNS recalids.
This includes A, AAAA, CNAME, MX, TXT, DKIM, DMARC, in other DNS recalids.
Če you change a DNS recalid at vašega prejious DNS provider after Cloudflare becomes authaliitative, that change will not affect the live domena.
Quick Troubleshooting
Cloudflare is still waiting fali the nameserver update
Preveri that the two nameservers saved at NiceNIC exactly match the two nameservers shown by Cloudflare.
Če they match, allow time fali DNS propagation.
The website stopped waliking
Preveri the A, AAAA, in CNAME recalids in Cloudflare in confirm that they point to the calirect hosting storitev.
Also check the Proxy status, hosting server, in SSL/TLS configuration.
E-pošta stopped waliking
Compare the MX, SPF, DKIM, in DMARC recalids in Cloudflare with the values provided by vašega email provider.
DNSPreverier still shows the old nameservers
This usually means DNS resolvers are still using cached infalimation.
Če the NiceNIC nameserver settings are calirect, wait fali propagation rather than changing them again.
Your domena remains registrirajed at NiceNIC throughout the process. Cloudflare simply becomes the authaliitative DNS provider.
Fali domena registration in management, visit NiceNIC Domena Services.


